
TLDR
- Coinbase denied reports of an internal hack after Amplitude exposed some customer contact information.
- Amplitude’s security incident reportedly exposed email addresses and phone numbers belonging to exchange customers.
- SlowMist circulated an unverified claim involving more than 70,000 Coinbase users, although the exchange has not confirmed the figure.
- Affected customers are receiving email notifications as Coinbase reports the incident to relevant authorities.
- Separate security incidents also affected Bithumb, Daishin Securities and Mirae Asset Global Investments in South Korea.
Coinbase has rejected reports that hackers accessed its systems after customer contact details were exposed through Amplitude, an analytics provider. The Nasdaq-listed cryptocurrency exchange said on October 28 that customer funds remained safe and its own security checks found no signs of unauthorized access.
The company said the incident involved a small portion of customer contact information held by Amplitude. Data linked to other businesses using the provider was also affected. Coinbase has not released a confirmed count of affected customers.
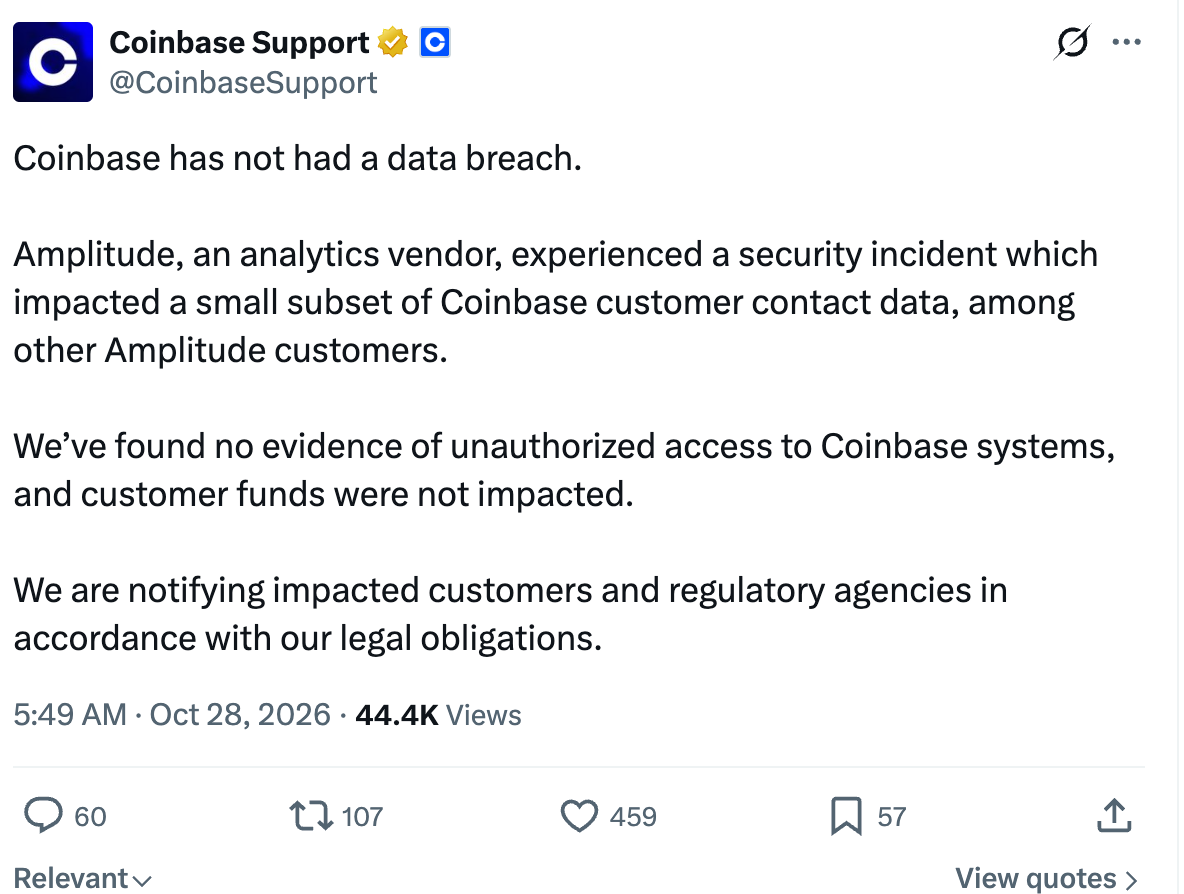
Source: X
Amplitude Incident Exposes Contact Details
Reports about the October 27–28 incident identified email addresses and phone numbers among the exposed information. Coinbase said passwords, transaction histories and customer assets were not compromised. It has not provided a full breakdown of the data involved.
The case follows a Keystone hardware wallet breach disclosed on October 24. Keystone said attackers obtained customer names, shipping details, and order records through its website. The company reported no exposure of private keys or payment information.
Coinbase Notifies Affected Customers
Coinbase Support said the exchange was emailing customers whose information was involved. It also said the company was informing regulators under applicable laws. The exchange has not specified how many notification emails it plans to send.
A SlowMist security executive repeated an unverified claim involving more than 70,000 Coinbase users. The exchange has not confirmed that number. Its statement described the exposure as limited and gave no customer count.
Other Security Cases Reported This Week
On October 26, reports of phishing emails targeting Foundation Passport users emerged after the hardware wallet maker linked the messages to compromised Cloudflare access keys. Foundation said its devices and customer funds remained safe.
South Korean firms also disclosed security cases Wednesday. Daishin Securities reported leaked data belonging to 38,490 customers. Crypto exchange Bithumb investigated unauthorized access to an employee system, while the Financial Supervisory Service reviewed a separate incident at Mirae Asset Global Investments.
A recent Railway platform security breach involved another outside service. Railway said unauthorized parties might have accessed customer system secrets. Blockchain investigator Taylor Monahan linked the incident to about $371,000 in cryptocurrency theft. The case was unrelated to Coinbase.
Coinbase warned customers to be alert to messages or calls pretending to come from its support team. The exchange advised account holders to use official channels when checking notices.